Case study / DevSecOps platform
Security checks that scale. One policy to maintain.
I designed and built a shared security scanning platform so application teams could adopt consistent checks through a small GitHub Actions workflow, while scanner configuration, policy, and reporting stayed centrally maintained.
My role: Sole designer and builder. Organization and application names are anonymized. Results below describe recorded implementation evidence, not a new production benchmark.
Recorded validation / September 2026
Less CI overhead in one measured comparison.
- PR scan wall time
- 120s → 86s
34 seconds shorter, approximately 28%.
- Billed job-minutes
- 4–5 → 2
50–60% fewer in this recorded comparison.
- Executed jobs
- 4 → 1
Consolidated scanning and policy evaluation.
The platform status record dated September 10, 2026 compares the first live consolidated PR run with the same repository’s run the previous day. This is one before-and-after observation. Workload and runner conditions were not controlled, so these figures are not a guarantee for other repositories or an estimate of organization-wide savings.
01 / The problem
Consistency without copying a platform into every repository.
Application repositories needed security checks without each team maintaining its own scanner versions, severity thresholds, and reporting logic. The platform also had to work within the organization’s existing GitHub capabilities and keep CI overhead manageable.
The engineering challenge was to separate finding collection from policy decisions, then make that shared contract reliable enough for repeated adoption.
02 / My contribution
A reusable delivery path with one verdict engine.
I built reusable PR and deep-scan workflows, scanner composite actions, result parsers, and a central policy engine. Scanner reports feed a common severity summary and normalized findings format; policy configuration determines the final verdict.
The scanning lanes cover secrets, static analysis, dependencies, infrastructure configuration, and Terraform linting. Deeper checks add optional container scanning, software bills of materials, and approved-target dynamic testing.
I also built the onboarding templates, interface documentation, exception handling, regression fixtures, and operational runbooks needed to maintain the platform after its initial rollout.
03 / Architecture
Collect evidence first. Apply policy once.
- Application workflow. A small caller selects the PR or deep-scan lane and scans its own repository.
- Shared scanner actions. Versioned tools write structured reports. They do not independently decide the policy outcome.
- Central verdict. One engine evaluates findings and scanner coverage, then publishes a summary and report artifacts.
Tool versions and checksums are pinned. Missing scanner coverage is evaluated alongside findings, so an incomplete scan cannot simply be treated as clean. Exceptions are repository-scoped and time-bound.
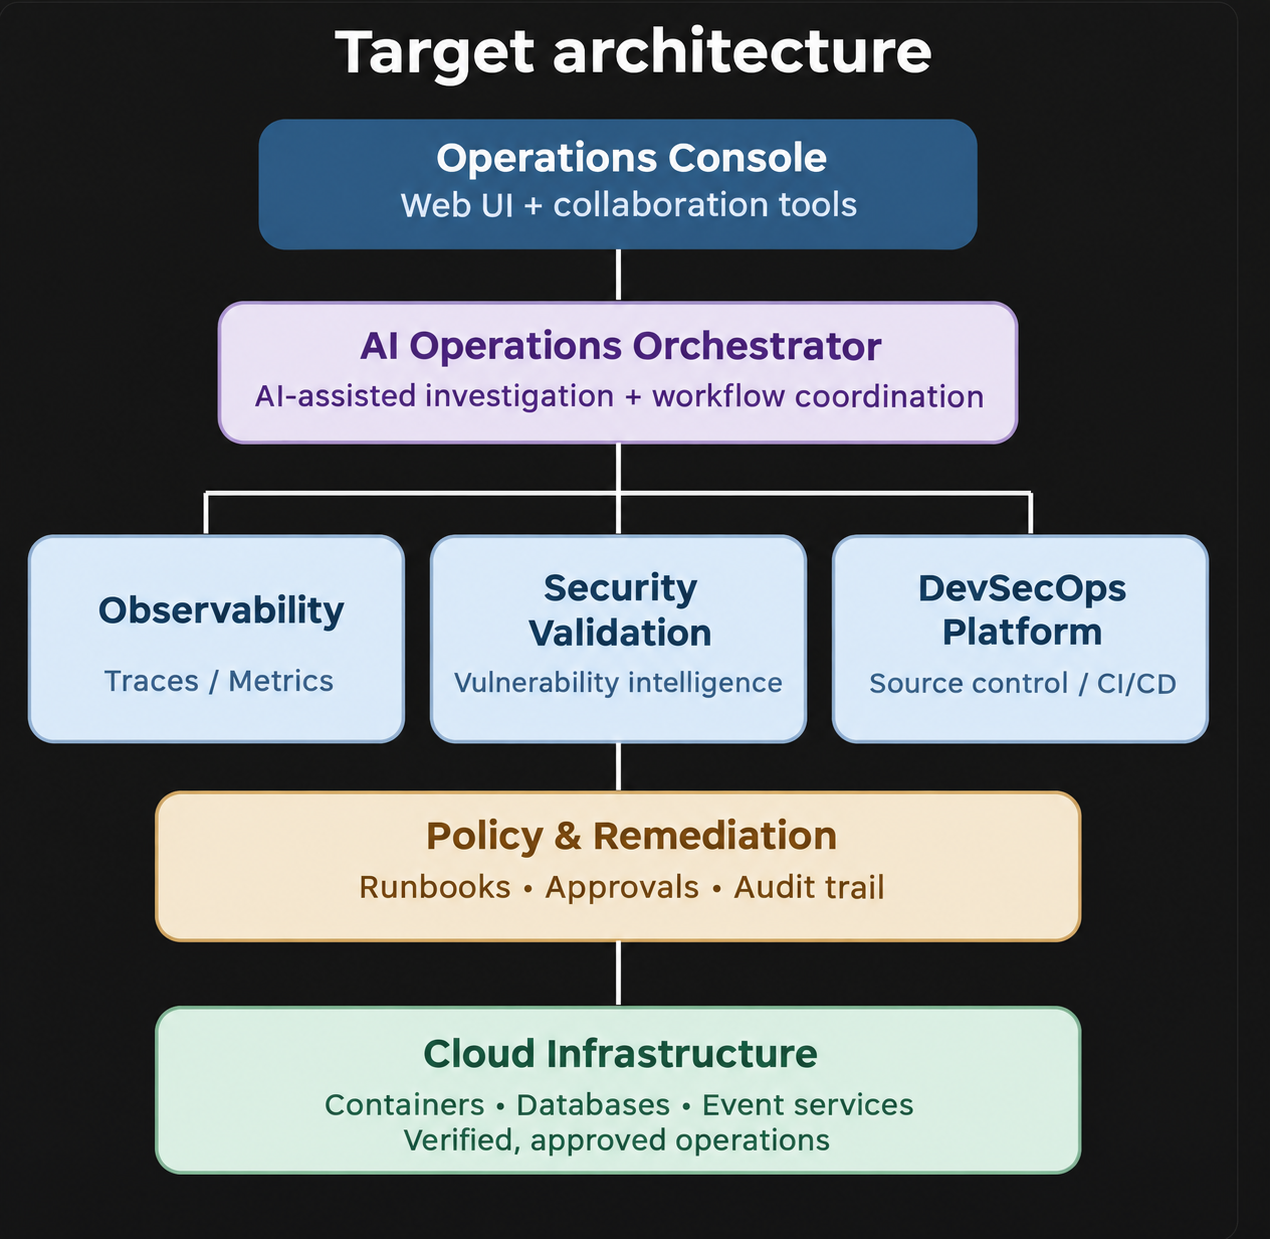
Target architecture
Intended operational design. This view includes planned capabilities and does not represent a fully implemented or verified deployment.
04 / Optimization
Reduce job overhead without removing the checks.
I introduced an optional consolidated PR lane that runs the scanning and final policy evaluation in a single job. Existing callers retain the original path unless they opt in.
Regression checks cover scanner coverage, gate behavior, artifacts, and failure reporting across the consolidated path. The recorded live comparison showed a smaller job footprint and shorter elapsed time; further measurements would be needed to establish a representative performance baseline.
05 / Results and boundaries
A shipped foundation, with explicit limits.
The delivered foundation moved reusable scanning, policy, and reporting into one maintained platform. Application repositories could consume that interface rather than carry the full implementation themselves.
Scan verdicts and merge enforcement are separate concerns. At the documented rollout stage, checks were advisory under the available repository controls; this case study does not claim that every failing check blocked a merge.
Later vulnerability-management, automated-remediation, and identity-migration work is outside the measured result here. I am not claiming a measured reduction in vulnerabilities, incidents, or remediation time from this comparison.
Related implementations
Workflow audit and infrastructure governance.
PipelineGuard: Audited GitHub Actions workflows for permissions and security practices, with findings presented in HTML reports.
CloudGuard IaC: Validated Terraform infrastructure changes against cloud governance policies and security controls.
These are related implementations; they are not presented as part of the measured scanning platform above.
Need consistent security checks across your repositories?
I can help design a workflow that fits your delivery process, operating constraints, and security policy.
Discuss your platform ↗